Online Poker Spyware Scandal
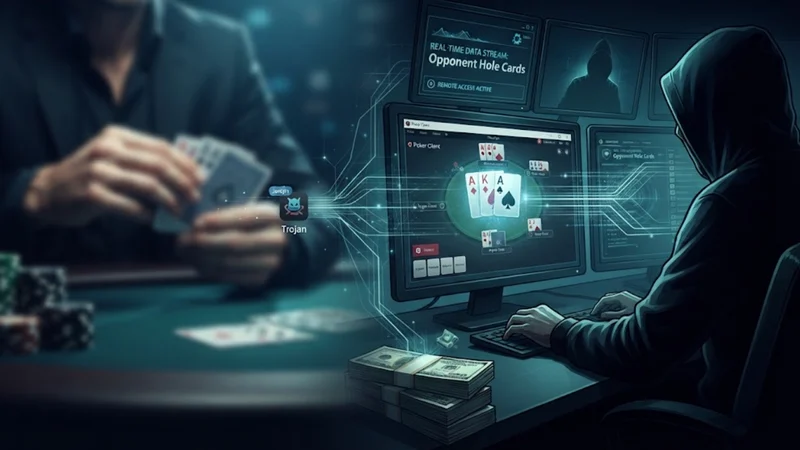
New details in a high-stakes online poker fraud: attackers compromised a multi-tabling tool's update system to install remote screen software and see opponents' hole cards.
How the Attack Worked
A high-stakes online poker fraud that allowed an attacker to view opponents' hole cards in real time did not involve hacking poker sites directly. Instead, the attacker installed a legitimate remote screen management tool, Mesh Agent, on victims' computers, gaining full oversight of selected professionals' cards.
The critical new development is how that software reached victims. Developers of the multi-tabling management tool Jurojin Poker confirmed that an attacker gained access to their server keys and an admin panel account. Between roughly June 2025 and June 2026, the attacker could place selected high-stakes players into special update groups. When those players launched Jurojin, they downloaded an altered update package containing a fake executable file that silently installed Mesh Agent in the background before running the legitimate, digitally signed Jurojin application. Because the software continued to function normally, players suspected nothing.
Jurojin also acknowledged a limitation in reconstructing the infection. Its database backups recorded group compositions only at certain intervals, so if the attacker added and removed a player quickly, no log record remained.
Victim Testimonies
Testimonies from affected professionals describe significant bankroll damage. Spanish high-stakes player Nacho Morón described a session in which an account linked to suspect Paul Gregg took $60,000 from him in a heads-up match within about 15 minutes. Morón estimates his total losses in the range of $100,000 to $200,000. He stressed that the opponent did not attack blindly: the person not only saw the cards but also played poker well, which is why the scheme took so long to uncover.
Manuel Saavedra reported that spyware was present on his computer for over a year. He documented losses of $59,275 on GGPoker against Gregg's account and a further €43,176 on ACR Poker. Saavedra described how the attacker would open heads-up tables for him and use knowledge of his cards as extra blockers against unaware players at the table.
The Data Review That Was Ignored
A key piece of the puzzle is an analysis compiled on September 1, 2026, by Mobius Poker founder Patrick Howard, after a friend nearly quit poker due to large losses against Gregg. Howard reviewed 32,780 hands played by Paul Gregg on GGPoker and sent a report to the site's management.
The review highlighted Gregg's overall win rate of +13.9 bb/100 on 10/20 6-max tables. The probability of an average player achieving that result purely through variance was calculated at 1 in 35,100. While in small pots (up to 40 bb) Gregg lost 802 bb, in pots over 150 bb he earned 2,497 bb, winning at showdown 74.3% of the time. In pots over 40 bb, he executed 153 aggressive actions on the river, reaching showdown 78 times and winning 59 of them, a 75.6% win rate that markedly exceeded the average win rate of other regulars at 58.2%. When calling river bets, he won 52 of 81 times, or 64.2%, against an average of 48.6%.
GGPoker did not act on the warning report for about a month, contacting Howard only on the evening of October 2, after Spanish magazine Poker Red published an article about the ignored report that spread across the X network. Howard later clarified that his report was a database review flagging anomalies for the site to monitor, not an accusation.
Different Platform Responses
The case highlighted sharp differences in how poker platforms responded. While some sites let suspicious accounts play for months or even years, CoinPoker detected and banned the account linked to Paul Gregg after about one week. Site ambassador Patrick Leonard said CoinPoker immediately blocked the account, seized over $100,000 and redistributed it to affected players. Nacho Morón confirmed that the site returned the $60,000 he lost in a heads-up match against Gregg. Gregg appealed to a regulator, but after CoinPoker presented evidence, he dropped the dispute. Leonard noted that at the time, no one knew the issue was larger and involved Jurojin, which he himself used.
ACR Poker moved quickly to introduce a solution. CEO Phil Nagy unveiled a new Screen Shield feature that blocks screen capture or sharing tools while the poker client is running. The site also sent hand histories for analysis and promised compensation to affected players.
Each site still reacts independently, and a lack of communication between operators is evident. Both Morón and Leonard criticized poker sites for not sharing information about banned cheaters. Morón compared the situation to Las Vegas casinos, where a cheater caught in one property is quickly known to all others. He argued that poker sites must learn to communicate in the same way.
What Players Should Do Now
The scandal raises critical security questions about support software. Although Jurojin's developers stated that malicious code was removed from their updates, security experts and Jurojin itself urge all players to check thoroughly for the presence of Mesh Agent. If there is any doubt, the advice is not simply to delete the program but to perform a complete Windows system reinstall and disk formatting. Players should also change passwords for gaming sites, email accounts and crypto wallets from another, uncompromised device.
Broader Lessons
For the poker community, the case underlines that third-party tools, even legitimate and widely used ones, can become an attack vector when an update pipeline is compromised. It also shows the value of independent hand-history reviews in flagging statistical anomalies, and the cost of slow or siloed responses between platforms. Until operators share ban lists and cooperate more closely, players remain the first and sometimes only line of defense.
FAQ
- The attacker installed a legitimate remote screen management tool called Mesh Agent on victims' computers, giving full oversight of their screens and cards. The software reached victims through a compromised update system of the multi-tabling tool Jurojin Poker.